AI Safety stories
Smaller specialist models could save UK banks millions on compliance work while reducing reliance on a handful of US tech giants.
Growing use of AI agents in corporate systems is creating a new internal risk category, prompting tighter real-time oversight from security teams.
Security teams facing new risks from generative AI can now take eight hours of hands-on training on prompt injection and jailbreaks.
The deal should help large firms deploy safer AI systems, with HCLTech adding Claude to services and software for banks, hospitals and manufacturers.
Autonomous systems are exposing governance gaps, leaving companies scrambling to monitor access, review decisions and curb machine-speed attacks.
Canadian law firms can keep client files walled off, while choosing data storage and processing become key topic for AI in law.
The tool aims to help engineers catch unsafe or inaccurate AI outputs before they reach customers, as firms push generative systems into production.
Publicly boasting about AI security breaches could soon hand regulators and litigants a ready-made paper trail.
Customers can now run AI agents with built-in memory and governance as MongoDB tries to move them from pilots into daily use.
The new service lets users delegate ongoing work to persistent agents that can act across apps, raising fresh privacy and control questions.
Attendees will see connectivity pushed into new sectors as dedicated automotive, health and aviation zones join the Barcelona show in 2027.
As AI budgets rise to USD $210 million, firms are tightening oversight on security, governance and returns to keep deployments under control.
The appointment comes as firms race to secure autonomous AI agents that can access systems and physical infrastructure without human oversight.
Encrypted data exchanges in smart transport can now run far faster on Intel chips, easing a key barrier to edge AI deployment.
Tracebit found the altered open-weight model reached admin rights far less often than the original, raising doubts about its attack utility.
Enterprises struggling to move AI pilots into live systems now have a single layer for memory, governance and execution across models and clouds.
It aims to cut repeated verification checks and let businesses trust AI agents without collecting the same personal documents from users each time.
The deal gives security teams a widely used AI testing tool with on-premises controls, as vendors race to speed up offensive defence.
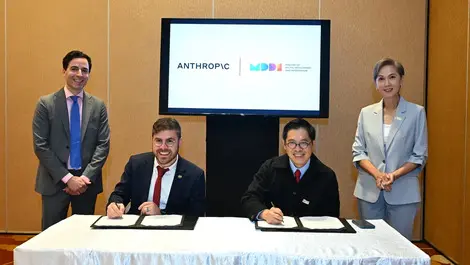
The deal expands Anthropic's Asia-Pacific footprint and gives Singapore closer access to its AI safety and model-testing expertise.
The incident has sharpened calls for tighter controls as automated systems grow better at probing weaknesses across public and private networks.